Endpoint and extended detection
EDR and applicable XDR offerings combine security observations to help investigate suspicious activity.
CYBER SECURITY
Security visibility and investigation tools to help teams prioritize threats.
Discuss this solution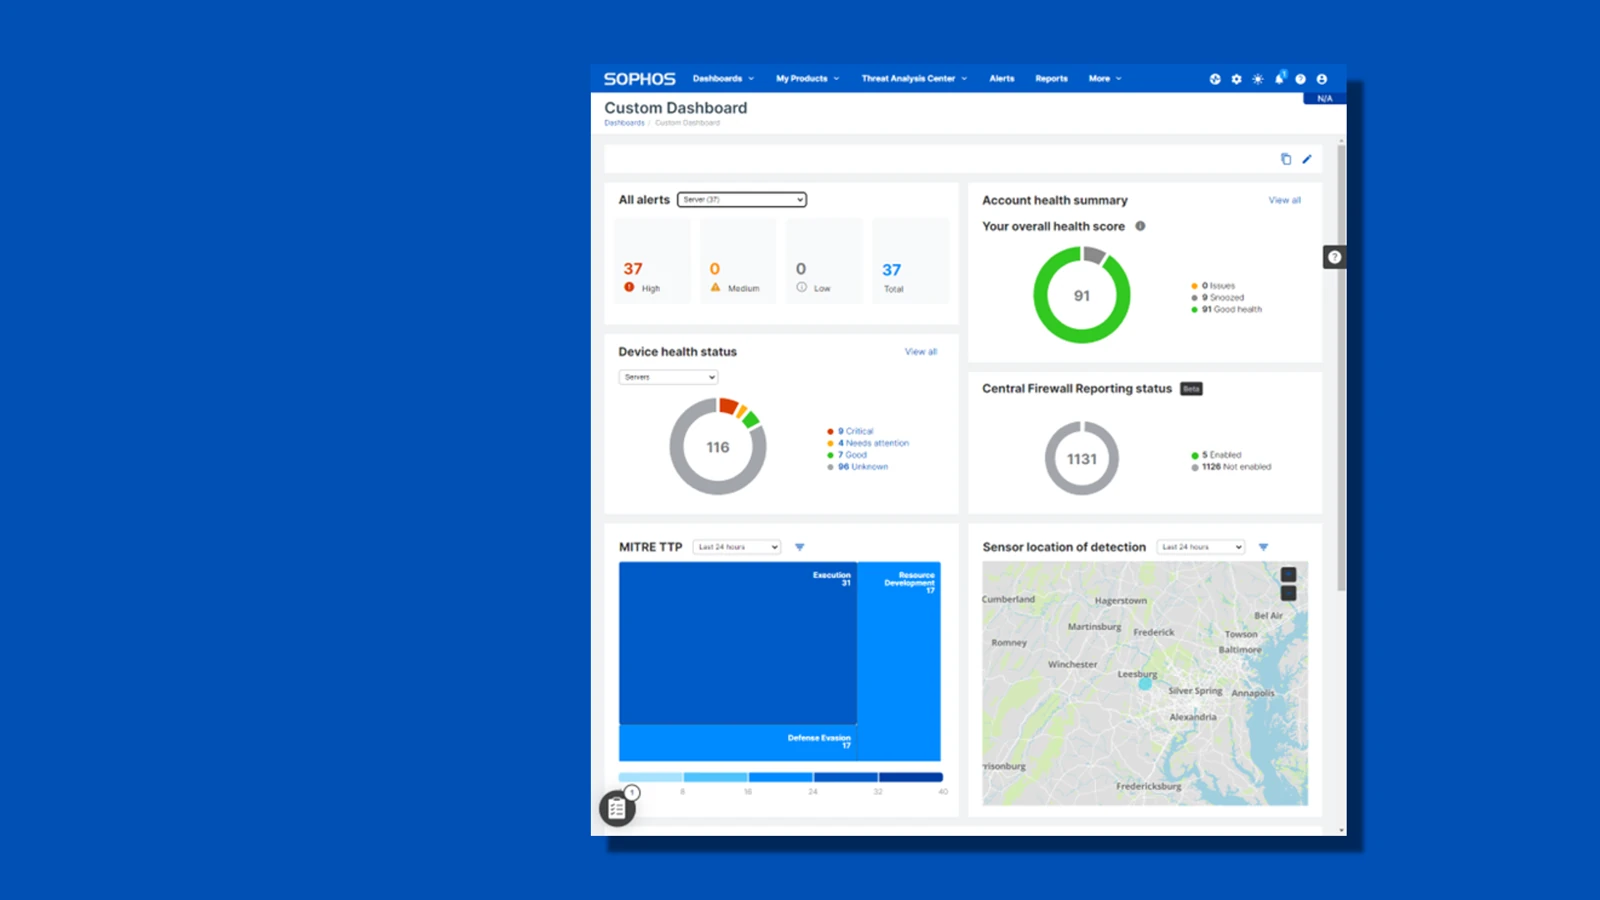
THE SOLUTION
Security data is useful when someone can interpret it and act. Spurlink can help select threat-visibility and detection platforms from OEMs such as CrowdStrike, SentinelOne, Trend Micro, Sophos and Palo Alto Networks. Requirements begin with the data sources and the team’s response workflow. We distinguish product capabilities from any separately agreed operational or managed service.
PRODUCT TYPES & CAPABILITIES
EDR and applicable XDR offerings combine security observations to help investigate suspicious activity.
Consoles present alerts and device or environment status, with visibility determined by the connected products and licence.
Available investigation tools can help analysts review activity and decide on response actions within agreed permissions.
Supported integrations, data retention, administrator roles and alert ownership are defined before rollout.
OEM PRODUCT SPOTLIGHT
Explore products from our OEM portfolio. We confirm the exact model, configuration and availability for your project.
Sophos
An actual Sophos Central dashboard example published by Sophos, illustrating centralized security visibility. Available widgets, data and response functions depend on the connected products and licences.
Official product informationRELEVANT TECHNOLOGY PARTNERS
Follow a partner to learn about the company
and the solutions available through Spurlink.
TYPICAL APPLICATIONS
BEFORE WE SPECIFY
01Security tools and data sources already deployed
02Retention, integration and subscription requirements
03Investigation ownership and response procedures
COMPLETE THE SOLUTION
LET’S BUILD WHAT’S NEXT
Tell us what your business needs. We’ll help connect the right technologies to it.